Use DNSSEC to boost your security.

As you know, the Domain Name System (DNS) infrastructure is the soul of pretty much everything on the Internet. There’s no web hosting, e-mail or messaging services, etc., that can exist online without the DNS.

And being that important, yes, the DNS has its Achilles heel: security. Its focus is not there, and that makes it vulnerable. But don’t worry, DNSSEC already exists! A reliable choice to boost security!
How does DNSSEC work?

(more…)

DNS SERVFAIL Explained: Causes and Step-by-Step Troubleshooting

DNS SERVFAIL Explained: Causes and Step-by-Step Troubleshooting

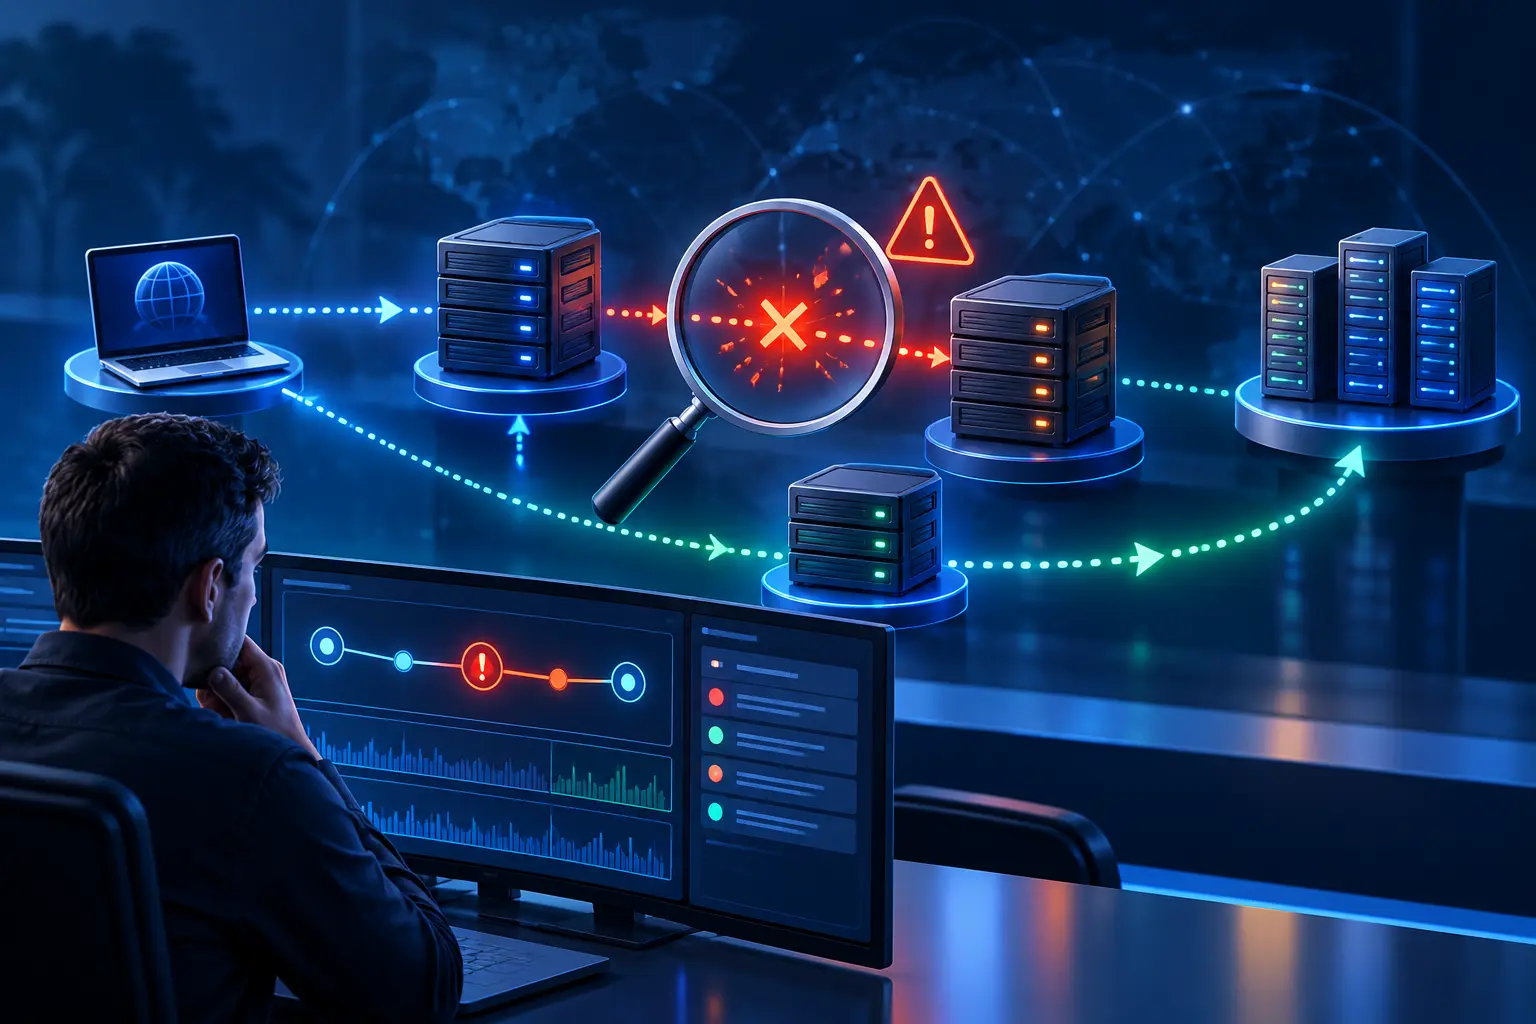
A DNS query that returns SERVFAIL tells you that the server could not complete the resolution process. The domain may exist and its records may be configured, but something prevented the responding resolver from producing a reliable answer. Because several different failures share this response code, the useful question is not simply “Is DNS down?” but “At which step did resolution fail?”

Effective troubleshooting compares resolvers, queries authoritative servers directly, checks delegation, reviews DNSSEC validation, and looks for timeouts or inconsistent data. This guide presents a repeatable process for narrowing the problem without changing records blindly.

What does DNS SERVFAIL mean?

SERVFAIL is DNS response code 2, meaning the name server encountered a failure while processing the request. It differs from NXDOMAIN, which says the queried name does not exist, and from NOERROR with an empty answer, which may mean the name exists but has no record of the requested type.

A recursive resolver can return SERVFAIL when it cannot reach an authoritative server, receives unusable responses, detects a broken delegation, fails DNSSEC validation, reaches a query limit, or encounters another internal error. The short response does not identify the cause by itself, so the next task is to collect evidence.

Start with a reproducible query

Use a command-line DNS tool so you can see the response code, flags, answering server, timing, and record sections. For example:

dig example.com A
dig example.com A @1.1.1.1
dig example.com A @8.8.8.8

The site’s existing Dig command guide explains the output and common query forms. Another beginner-friendly reference is this Dig command walkthrough. Both are useful before interpreting differences between recursive and authoritative answers.

Record the exact name, type, resolver, time, and result. A failure for an AAAA query does not prove that the A record fails, and a cached answer from one resolver does not prove that every resolver sees the same state.

Compare multiple recursive resolvers

Ask at least two independent recursive resolvers for the same name and type. If one returns a valid answer while another returns SERVFAIL, the zone may be healthy and the problem may involve cached state, DNSSEC validation, transport behavior, or a resolver-specific issue. If every resolver fails, focus on delegation and the authoritative service.

Also compare the failing network with a different connection. A local firewall, filtering product, VPN, or router can affect DNS traffic. Testing from another network helps separate a domain-wide fault from a client or access-network problem.

Trace the delegation path

The +trace option follows delegation from the root toward the target zone:

dig +trace example.com A

Look for the point where useful responses stop. Common delegation problems include nameservers listed at the parent that do not serve the child zone, missing glue for in-bailiwick nameservers, unreachable server addresses, and inconsistent NS sets between parent and child.

A delegation can appear correct in a control panel while the live parent zone contains older or different data. Query the parent-side information and each delegated nameserver rather than relying only on the provider interface.

Query authoritative servers directly

After identifying the delegated nameservers, resolve their addresses and query each one:

dig example.com A @ns1.example.net
dig example.com SOA @ns1.example.net
dig example.com NS @ns1.example.net

A healthy authoritative server should answer consistently and set the authoritative-answer flag for data in its zone. If one server times out or has an older SOA serial while the others respond correctly, investigate synchronization, firewall rules, routing, and service health on that server.

Test over both UDP and TCP when the symptoms suggest truncation or transport filtering:

dig example.com A @ns1.example.net
dig +tcp example.com A @ns1.example.net

DNS normally begins with UDP for many queries, but TCP is required in several situations and must not be blocked indiscriminately. Large responses, DNSSEC data, and retry behavior can expose a firewall that permits UDP while dropping TCP.

Check DNSSEC validation

A DNSSEC-validating resolver returns SERVFAIL when it cannot build a valid chain of trust or verify signed data. Typical causes include an incorrect DS record at the parent, expired signatures, missing signatures, a key rollover performed in the wrong order, or inconsistent signed responses across authoritative servers.

Compare a normal query with one that disables validation checking at the diagnostic client:

dig example.com A +dnssec
dig example.com A +dnssec +cdflag

If a validating lookup fails but the checking-disabled query returns data, investigate DNSSEC rather than treating the returned data as proof that the zone is healthy. Review the site’s guide on how to use DNSSEC securely for the purpose of signatures and the chain of trust.

Do not remove the parent DS record as an unplanned first response. A DNSSEC repair must coordinate the child-zone keys, signatures, and parent delegation. Improper changes can extend the outage or remove the intended protection.

Inspect the zone for structural problems

Authoritative data can be reachable yet still lead resolvers into failure. Check for:

  • CNAME loops: One alias ultimately points back to itself through one or more names.
  • Excessive alias chains: Long chains consume resolver work and introduce more failure points.
  • Broken dependencies: An NS, MX, or CNAME target depends on a name that cannot be resolved.
  • Inconsistent zone copies: Authoritative servers publish different records or SOA serials.
  • Invalid server configuration: The service loads an incomplete zone, rejects queries, or is not authoritative for the expected name.

Validate the zone file with the authoritative server software’s checking tools before loading it. After a change, query each authoritative server directly to confirm that the intended version is active everywhere.

Separate propagation from failure

DNS caches can temporarily preserve older positive or negative answers after a planned change. That behavior is often described as propagation, but an actual SERVFAIL usually indicates that a resolver could not complete or validate resolution, not merely that it retained an old value.

The article Understanding DNS propagation explains TTL-driven cache timing. Use TTL and cache history to interpret different answers, but continue investigating when resolvers consistently return a failure code.

Look for Extended DNS Error details

Some resolvers attach an Extended DNS Error option that provides a more specific reason, such as DNSSEC bogus data, no reachable authority, a network error, or a response considered stale. Recent versions of dig may display this information in the response.

Extended error text is diagnostic context rather than a replacement for the DNS response code, and support varies. The standardized codes and their intended use are defined in RFC 8914: Extended DNS Errors.

A practical SERVFAIL checklist

  1. Repeat the exact query and save the full output.
  2. Compare at least two independent recursive resolvers.
  3. Run a trace and verify the parent delegation and glue.
  4. Query every authoritative nameserver directly for A, SOA, and NS data.
  5. Test UDP and TCP reachability.
  6. Compare DNSSEC-validating and checking-disabled diagnostic results.
  7. Inspect aliases, dependencies, SOA serials, signatures, and server logs.
  8. Fix the identified layer, then retest authoritative and recursive paths.

Conclusion

DNS SERVFAIL is a symptom, not a root cause. The fastest route to a repair is to divide resolution into layers: client and network, recursive resolver, delegation, authoritative servers, zone data, and DNSSEC validation. Controlled queries at each layer reveal whether the fault is local, cached, unreachable, inconsistent, or cryptographically invalid—allowing you to correct the real problem instead of making speculative DNS changes.

DNS Amplification Attacks: How They Work and How to Reduce the Risk

DNS Amplification Attacks: How They Work and How to Reduce the Risk

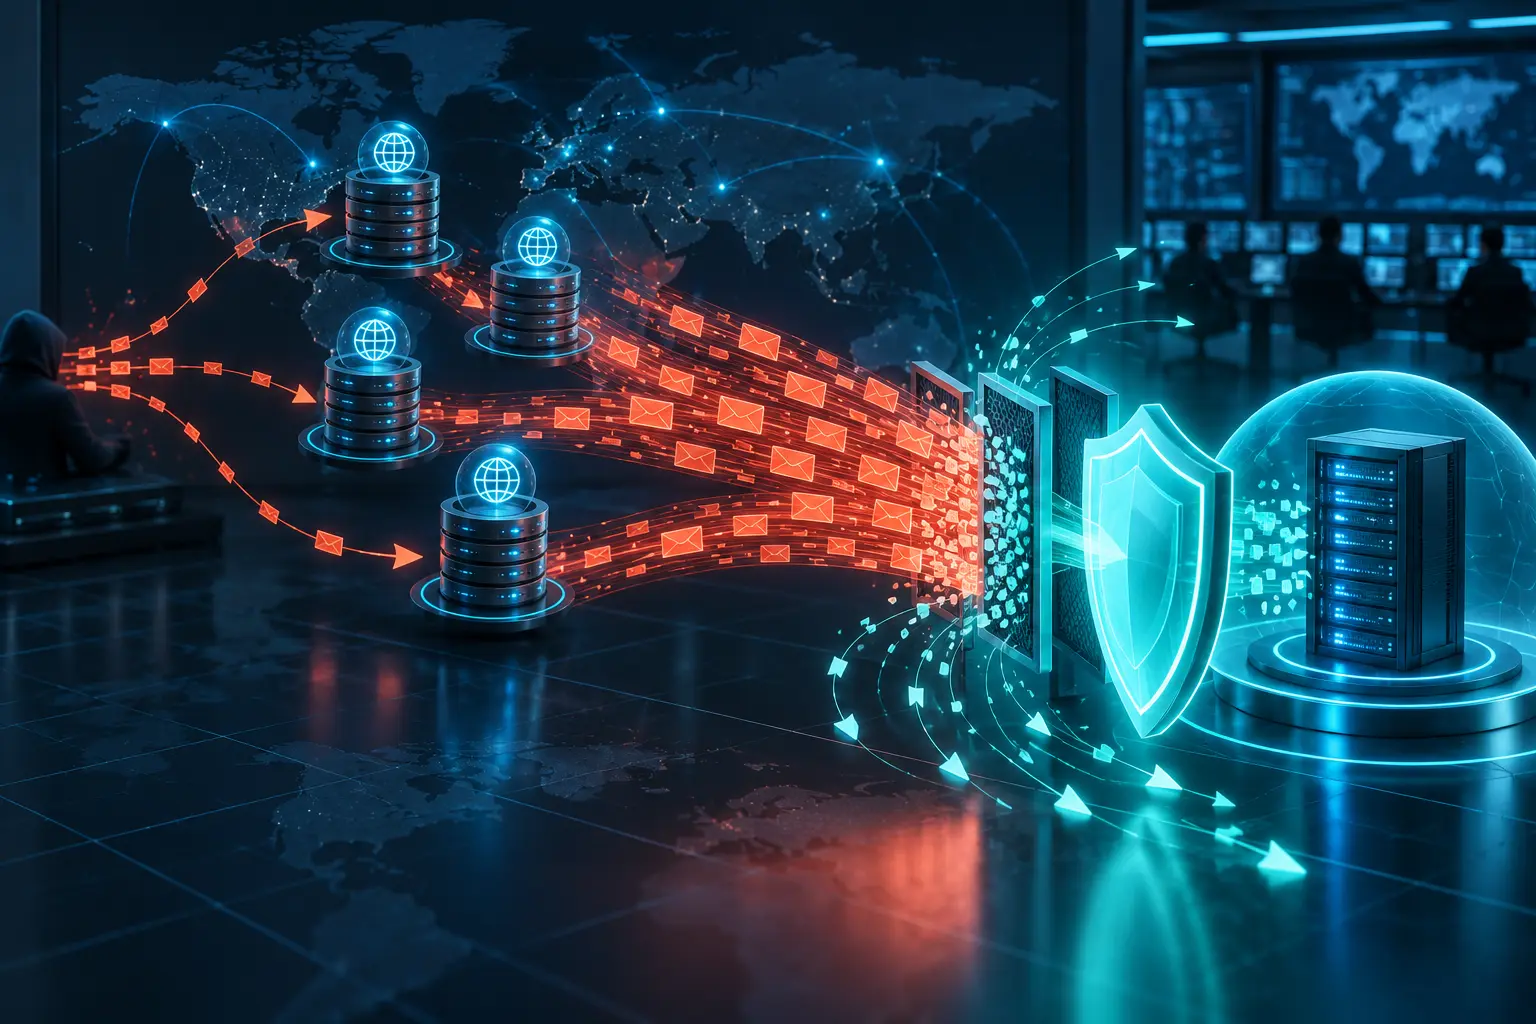
A DNS amplification attack turns ordinary DNS infrastructure into a source of unwanted traffic aimed at a victim. The attacker sends relatively small queries with a forged source address, and misconfigured or exposed DNS servers send larger responses to that address. When the process is repeated through many servers, the victim receives a flood it never requested.

This attack combines two ideas: reflection hides the true source by directing replies elsewhere, while amplification makes the returned traffic larger than the traffic sent by the attacker. Understanding both parts helps DNS operators avoid becoming reflectors and helps organizations prepare defenses for large inbound floods.

How DNS reflection and amplification fit together

Reflection redirects the reply

Many traditional DNS exchanges use UDP. Because UDP does not establish a connection before data is sent, networks that permit source-address spoofing can allow a packet to claim that it came from the victim’s IP address. A DNS server then sends its answer to the forged address rather than to the attacker.

Amplification increases the traffic volume

A DNS response can be larger than its query. The exact difference depends on the question, the available records, protocol options, and the server’s response. Attackers seek situations where small requests trigger significantly larger replies, multiplying the traffic that reaches the victim.

The underlying resolver role is explained in What is the role of the Recursive DNS server?. A recursive resolver should normally serve an intended group of clients. When it accepts recursive queries from arbitrary Internet addresses, it can become an open resolver and a useful reflector for abuse.

Why DNS is attractive for reflection attacks

  • DNS is widely deployed. Authoritative and recursive servers are essential parts of Internet infrastructure.
  • UDP supports efficient queries. That efficiency also means the server can respond without a connection handshake.
  • Some resolvers are exposed unnecessarily. Incorrect access controls may allow anyone on the Internet to request recursion.
  • Responses vary in size. Some legitimate DNS answers contain multiple records, signatures, or other data and are much larger than the request.
  • Source spoofing still exists. Networks that do not filter packets with implausible source addresses enable reflection.

Large DNS responses are not inherently malicious. DNSSEC signatures, IPv6 records, mail records, and other legitimate data can all increase response size. The security problem is the combination of spoofed traffic, exposed services, and repeated requests designed to create a flood.

Signs that a resolver may be abused

Operators should look for behavior that differs from the server’s normal client and query profile. Possible indicators include:

  • a sudden increase in queries from many unrelated or unexpected addresses;
  • repeated requests for the same names or record types;
  • an unusual ratio of outbound response bytes to inbound query bytes;
  • high UDP response volume without a matching increase in legitimate users;
  • queries arriving on interfaces or from networks that should not use recursion;
  • bandwidth, CPU, or packet-rate alerts on DNS systems and edge devices.

These signals require context. A public authoritative server naturally receives queries from many networks, while a corporate recursive resolver should have a much narrower client population. Baselines and role-specific alerting are more useful than one universal threshold.

How recursive DNS operators can reduce abuse

Disable open recursion

Recursive service should be limited to authorized clients through access-control lists, network boundaries, and firewall policy. If a server is intended only for an internal network, it should not answer recursive requests from the public Internet.

Separate recursive and authoritative roles

Running recursion and public authoritative service on separate systems makes access policy clearer and reduces the chance that a necessary public-facing server accidentally provides recursion to everyone.

Keep DNS software and policy current

Apply supported software updates, remove unnecessary features, review listening interfaces, and test the service externally. Configuration drift can expose recursion even if the original deployment was secure.

Monitor response volume and client eligibility

Track packets, bytes, response sizes, query types, source networks, and rejected requests. Alerts should highlight traffic from outside approved client ranges and sudden changes in the response-to-query ratio.

How authoritative DNS operators can help

Public authoritative servers must answer Internet queries, so they cannot use the same client allowlist as private resolvers. They can still reduce abuse and improve resilience:

  • Use response rate limiting where appropriate. Carefully configured RRL can reduce repeated similar responses without blocking normal traffic.
  • Serve minimal necessary data. Avoid unnecessary additional records and remove obsolete zone content while preserving standards-compliant answers.
  • Distribute capacity. Anycast, multiple locations, and independent authoritative providers can prevent one site from becoming the only bottleneck.
  • Monitor answer correctness as well as availability. A reachable server returning inconsistent data is still unhealthy.
  • Prepare upstream mitigation. Large floods may need filtering or scrubbing before they reach the authoritative network.

A Managed DNS service may provide distributed capacity, monitoring, and mitigation features, but organizations should verify the actual architecture and incident process rather than relying only on a product label.

Source-address validation is essential

Reflection depends on forged source addresses. Network operators can reduce this capability by filtering traffic whose claimed source should not be reachable through the interface where it arrived. This practice is often described as ingress or egress filtering, depending on where the check occurs.

DNS administrators cannot solve global source spoofing alone. Internet service providers, hosting networks, cloud platforms, and enterprise edge operators all contribute by validating source addresses close to where traffic enters their networks.

Protecting an organization that is the target

A victim cannot directly reconfigure the third-party reflectors sending the traffic. Defensive preparation should therefore focus on absorbing, distributing, or filtering the flood before it overwhelms the destination:

  • coordinate DDoS procedures and escalation contacts with network providers;
  • use upstream scrubbing or managed protection sized for realistic attack volumes;
  • distribute public services across independent locations and networks;
  • monitor packet rate and bandwidth, not only application CPU and request logs;
  • maintain tested incident runbooks for routing, filtering, communication, and recovery;
  • preserve evidence and timestamps for provider coordination and later analysis.

The historical examples in 4 DDoS attacks in recent history show why mitigation capacity and coordination must exist before an incident starts.

Controls that address different problems

Several useful DNS controls are sometimes confused with amplification defenses:

  • DNSSEC authenticates DNS data but does not prevent a server from receiving spoofed queries. Its larger signed responses also make careful server policy important.
  • Short TTL values change cache duration; they do not stop reflected traffic.
  • DNS caching improves efficiency for clients but does not secure an open resolver exposed to arbitrary users.
  • Blocking all UDP DNS can break legitimate service and force different failure modes. Defenses should be role-aware and standards-compatible.

A practical defensive checklist

  1. Inventory every DNS server and identify whether it is recursive, authoritative, or both.
  2. Test from outside approved networks to confirm that private recursion is not publicly available.
  3. Restrict recursive clients and separate public authoritative service where possible.
  4. Enable suitable rate controls, logging, and traffic baselines.
  5. Ask connectivity providers how they implement source-address validation.
  6. Confirm DDoS escalation paths, mitigation capacity, and monitoring coverage.
  7. Retest after software, firewall, network, or DNS configuration changes.

Conclusion

DNS amplification attacks succeed when forged queries can reach servers that return larger replies to the victim. No single control solves the entire problem. Restricting recursion, validating source addresses, minimizing unnecessary responses, applying rate controls, distributing authoritative capacity, and preparing upstream mitigation each remove a different part of the attack path.

For an overview of this and other threats, see 5 DNS attacks that could affect you. Detailed guidance for preventing recursive nameservers from becoming reflectors is provided in RFC 5358: Preventing Use of Recursive Nameservers in Reflector Attacks.

Popular Load balancing approaches

Load balancing: What does that mean?

DNS Load balancing uses domain settings to distribute client requests around server computers. Any website, email service, or another Internet-based service can be connected to the domain.

You might anticipate receiving a lot of requests if you run a significant and well-known website. It must also respond to queries accurately and quickly, provide up-to-date information, and be quick. Here, the idea of traffic balancing is put into use.

DNS load balancing vs. Hardware load balancing

(more…)

MX record – What is it?

MX record or Mail Exchanger is one of the most essential Domain Name System record types. In this article, we will take a detailed look at its main purpose, how it looks and why it is so beneficial. Let’s start.

What is a DNS record?

DNS records are text instructions. They provide them to the DNS server, allowing it to determine which domain names each IP address belongs to. They’re small and easy to update, and their size varies depending on the query type. We are humans, and we remember domain names, not different and complicated IP addresses. But computers can’t read these domain names. So they must rely on records to comprehend and decipher words. That is, they turn the text file into machine-readable numbers.

MX record – the main purpose

MX record is one of the most utilizing DNS records. Its abbreviation stands for Mail Exchange. What does it mean? It contains information for sending email servers, such as the name of the responsible server for accepting emails on behalf of the domain. So it establishes a link between the domain name and the inbound mail server.

How to create MX records?

(more…)

DNS record types every beginner should know

For most beginners, the concept behind DNS could seem complex—especially for those without a technical background. However, here are some essential DNS record types that will help you manage your DNS easily.

A record

Probably the A (address) record is the most popular of all DNS record types. The reason for that is simply because its purpose is very specific and also very fundamental. The A record links the hostname to the corresponding IP address (IPv4). That way, people remember just domain names and don’t bother with IP addresses.

DNS A record fully explained

(more…)

DNS zone: Explained for beginners

The DNS zone is a plain text file containing all of the DNS records for the domain. The DNS, as you may know, is a complicated system that serves as a global database of domain names and IP addresses. As a result, a Domain name system zone is essential for the domain name system to function.

DNS zone – meaning

The DNS zone is a minor but essential part of the Domain Name System (DNS) namespace. It’s an operating segment that lets DNS administrators control and regulate their networks. There are likely a lot of DNS zones that use the same DNS server as you. Therefore, it is easier to handle the entire namespace.

Furthermore, the complete Domain Name System (DNS) exists due to these divisions.

What is Master DNS zone and why do you need it?

(more…)

​Dig command: Purpose, Syntax, and Examples

If you are a Linux user, you have a great built-in network diagnostic tool – the Dig command. It is a simple software that you can use through the Terminal. It serves various network diagnostics.

​Purpose of the Dig command.

Dig command is a DNS utility that is available on Linux. The purpose of the Dig command is to be able to get information about your domain quickly. You can probe different DNS record types, see if the DNS propagation has ended, and check the parameters of a particular DNS record. You can also see which are the name servers that are authoritative for a domain and see if they respond correctly.

(more…)

Understanding DNS propagation.

Technology is the keystone of modern life. It has made many things easier! It has also accelerated many processes and daily tasks to the point we humans now expect everything to happen at light speed. Today, waiting three seconds can be a reason to abandon a web search or a website because that feels “too long”.

The reality is, massive processes, even with advanced technology involved, still, require much more than milliseconds to be completed accurately. Like DNS propagation!

What’s DNS propagation?

DNS propagation is the time period that it takes to update DNS modifications across the Internet.

DNS propagation – How to check it?

(more…)

DNS spoofing – How to prevent it?

The creation of the Domain Name System (DNS) in the early 1980s was a big achievement. Its design considered a vast functionality, but security was not a priority almost four decades ago. The problem is that criminals knew it, and soon they took advantage of this weak point. Criminals developed different attacks using the DNS, like the dangerous DNS spoofing. 

What is DNS spoofing?

DNS spoofing is a hacking attack. Criminals enter spoofed or forged entries or DNS records into the cache of a recursive server to respond to DNS users’ queries with a spoofed record, for instance, a forged IP address. This way, legit traffic is maliciously directed to dangerous destinations (forged websites). Once there, users can be pushed to type sensitive data (passwords, bank card details, etc.) for criminals to take advantage of later.

(more…)

What is the role of the Recursive DNS server?

We could talk a lot about DNS functionality, however, let’s concentrate at the moment on one major DNS component, the recursive DNS server. 

Recursive DNS server explained.

The Recursive DNS server is responsible for searching for data that is required for answering the queries of the users. Recursion in computing is associated with a method for solving a problem. That means a program or solution is going to repeat itself until it reaches the goal.

Recursion and Iteration: Explaining the Dynamic Duo

(more…)